

Microsoft 365 Copilot and Agent Administration Fundamentals (beta) AB-900 Exam Questions
Preparing for the AB-900 exam is simple with ExamsDay. We offer easy-to-understand study materials that help you learn the most important exam topics. You can study using our PDF questions, practice online with a real exam-style test, or use the desktop practice software. Choose the study method that works best for you and prepare at your own pace.
At ExamsDay, we keep our AB-900 practice questions up to date. Whenever the exam syllabus or objectives change, we update our study materials so you always learn the latest topics. This helps you save time, avoid outdated content, and feel more confident when you take your exam.
HOTSPOT Select the answer that correctly completes the sentence.
Answer
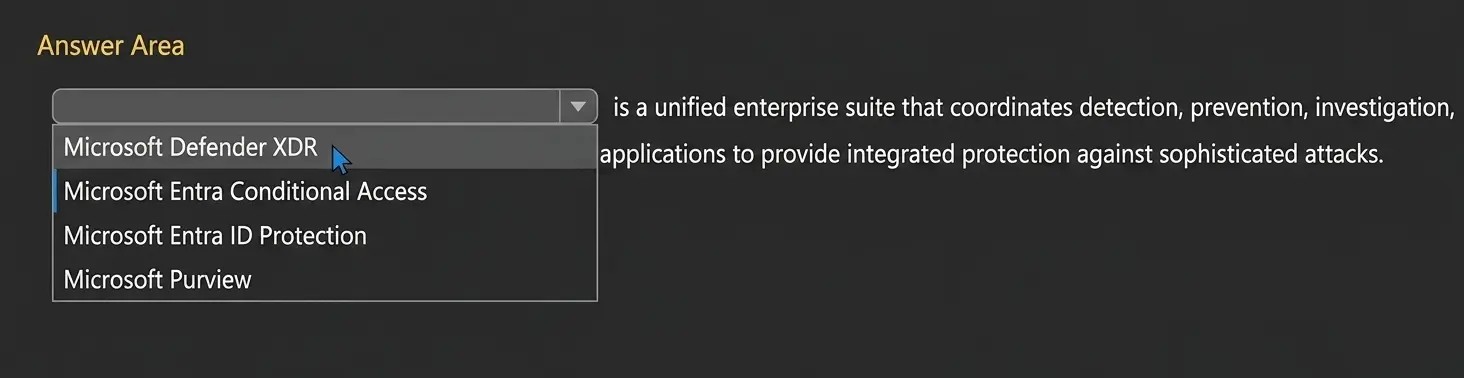
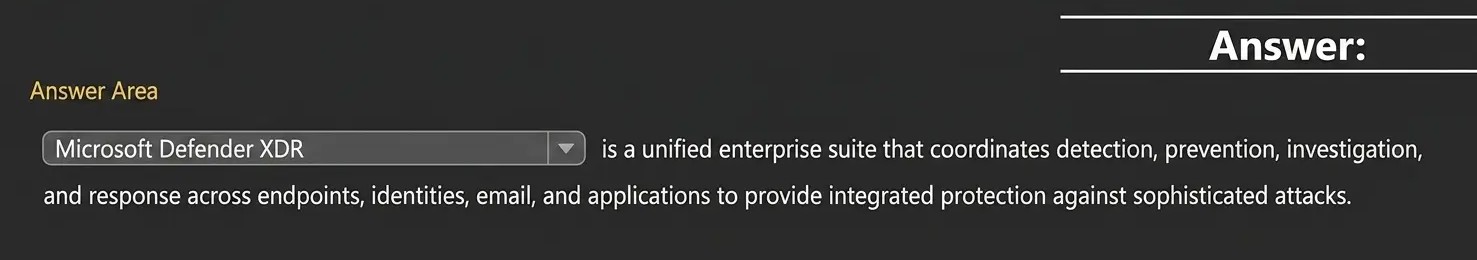
The correct answer is Microsoft Defender XDR. Microsoft Learn defines Microsoft Defender XDR as a unified pre- and post-breach enterprise defense suite that natively coordinates detection, prevention, investigation, and response across endpoints, identities, email, and applications to provide integrated protection against sophisticated attacks. That wording matches the sentence in the question almost exactly, which makes this the clearly correct choice. The other options do not fit that definition. Microsoft Entra Conditional Access is Microsoft’s Zero Trust policy engine used to evaluate signals and enforce access policies, not a cross-domain threat detection and response suite. Microsoft Entra ID Protection focuses on detecting and responding to identity risks such as risky sign-ins and risky users. Microsoft Purview is Microsoft’s portfolio for data governance, data security, and compliance. None of those products is described by Microsoft as coordinating detection, prevention, investigation, and response across endpoints, identities, email, and applications in the same integrated XDR manner. Therefore, the only answer that correctly completes the sentence is Microsoft Defender XDR.
Your organization has a Microsoft 365 subscription. Which two tasks can you perform by using the Exchange admin center? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
Correct Answer: A, D
The correct answers are A and D because both tasks are supported directly in the Exchange admin center (EAC). Microsoft Learn states that administrators can manage mail flow rules in Exchange Online from the EAC under Mail flow > Rules, which includes creating and managing transport rules for organizational email handling. Microsoft Learn also states that administrators can create shared mailboxes in the EAC under Recipients > Mailboxes, where a shared mailbox can be added and then delegated to users. Option B is incorrect because adding a custom domain is normally done in the Microsoft 365 admin center, specifically on the Domains page. Although Exchange can later work with accepted domains and related mail flow settings, the act of adding and verifying a custom domain is not an Exchange admin center task. Option C is incorrect because license assignment is handled through Microsoft 365 or Microsoft Entra administrative tools, not the Exchange admin center
HOTSPOT
Chose the answer
Answer
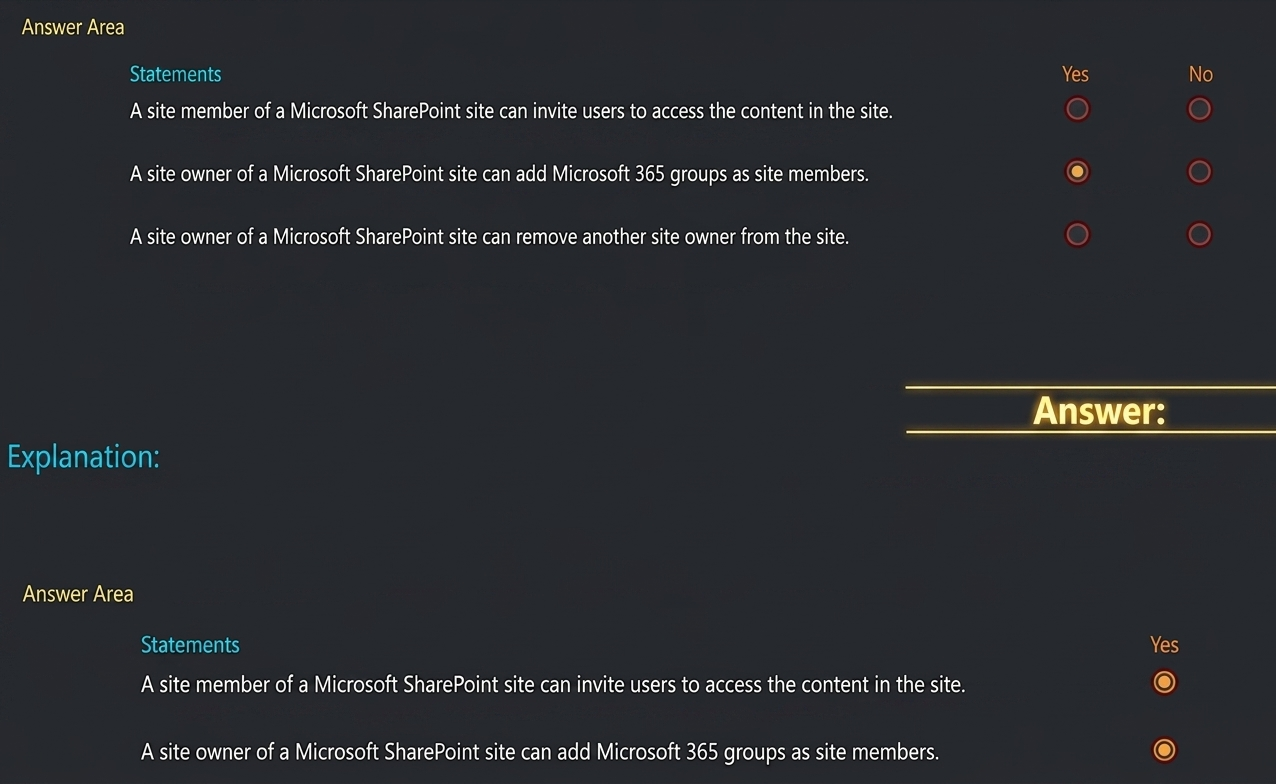
The correct selections are Yes, Yes, Yes. For statement 1, Microsoft Support explains that if you are not a site owner, you might still be able to invite other people to the site, although the invitation can generate an access request that a site owner approves or declines. Microsoft also states that site users have the opportunity to invite other people to collaborate on sites, unless that feature is disabled. That makes the statement true. For statement 2, Microsoft Learn states that in SharePoint you can give people permissions to a site by adding individual users, security groups, or Microsoft 365 groups to one of the three SharePoint groups, including the Members group. That directly supports the statement. For statement 3, Microsoft documents that site ownership and membership can be managed by adding or removing owners, members, site owners, site members, and site visitors. For group- connected sites, Microsoft also documents that owners can manage group ownership and remove owner status. Therefore, a site owner can remove another site owner, provided at least one owner remains.
Your organization has a Microsoft 365 subscription.
You need to generate a report that shows the permissions and active sharing links of content stored in Microsoft OneDrive accounts.
What should you use?
Correct Answer: A
The correct answer is A. Data access governance in the SharePoint admin center . Microsoft Learn documents Data access governance reports in the SharePoint admin center as the reporting solution used to understand data exposure, including permission structure and sharing link activity . Microsoft specifically states that the site permissions snapshot report provides visibility across SharePoint and OneDrive sites , helping administrators understand current permissions exposure, and that separate reports are created for SharePoint and OneDrive . Microsoft also documents sharing links activity reports as part of Data access governance for monitoring link-sharing activity, and notes that OneDrive support is available through PowerShell for those reports. Together, this is the Microsoft reporting capability aligned with permissions and active sharing links for OneDrive content.
The other options do not fit this requirement. Microsoft 365 admin center reports focus mainly on usage and activity reporting, not detailed permissions and sharing-link governance. Defender Audit is for security investigation activity, and Purview eDiscovery is for legal and investigative content search, not for generating OneDrive permissions and sharing-link governance reports. Therefore, the best Microsoft-documented answer is Data access governance in the SharePoint admin center .
You need to identify files and emails that contain social security numbers (SSNs) and credit card numbers. What should you use in the Microsoft Purview portal?
Correct Answer: B
The correct answer is B. Data explorer. Microsoft Learn states that Data explorer in Microsoft Purview shows a current snapshot of items that have been classified as a sensitive information type in your organization. Microsoft’s sensitive information type documentation specifically lists examples such as social security numbers and credit card numbers, which means Data explorer is the appropriate portal feature for identifying files and emails that contain those data types. Data explorer is designed to help administrators see where sensitive data exists across supported Microsoft 365 locations.
The other options are less appropriate for this task. Information Protection reports focus more broadly on label and protection reporting. Information Protection policies are for configuring classification and protection behavior, not for finding existing files and emails containing SSNs or credit card numbers. Activity explorer is primarily used to review user and policy-related activities, such as label changes or DLP events, rather than to provide the direct sensitive-data inventory view requested here. Since the question asks to identify the files and emails containing specific sensitive information types, Microsoft’s documented answer is Data explorer.